Career data is people data. We treat it that way.
Career conversations, development plans and skills assessments are some of the most personal information an employer holds. Here's exactly how we protect it, what we've built, and what we're still building.
Someone has probably sent you this link because your organisation is considering CareerPaths, and the questions about data protection, hosting, AI and sub-processors are now yours to answer.
Everything your security, IT and procurement teams will ask for — published before you commit, not after you've signed.
How the platform is secured.
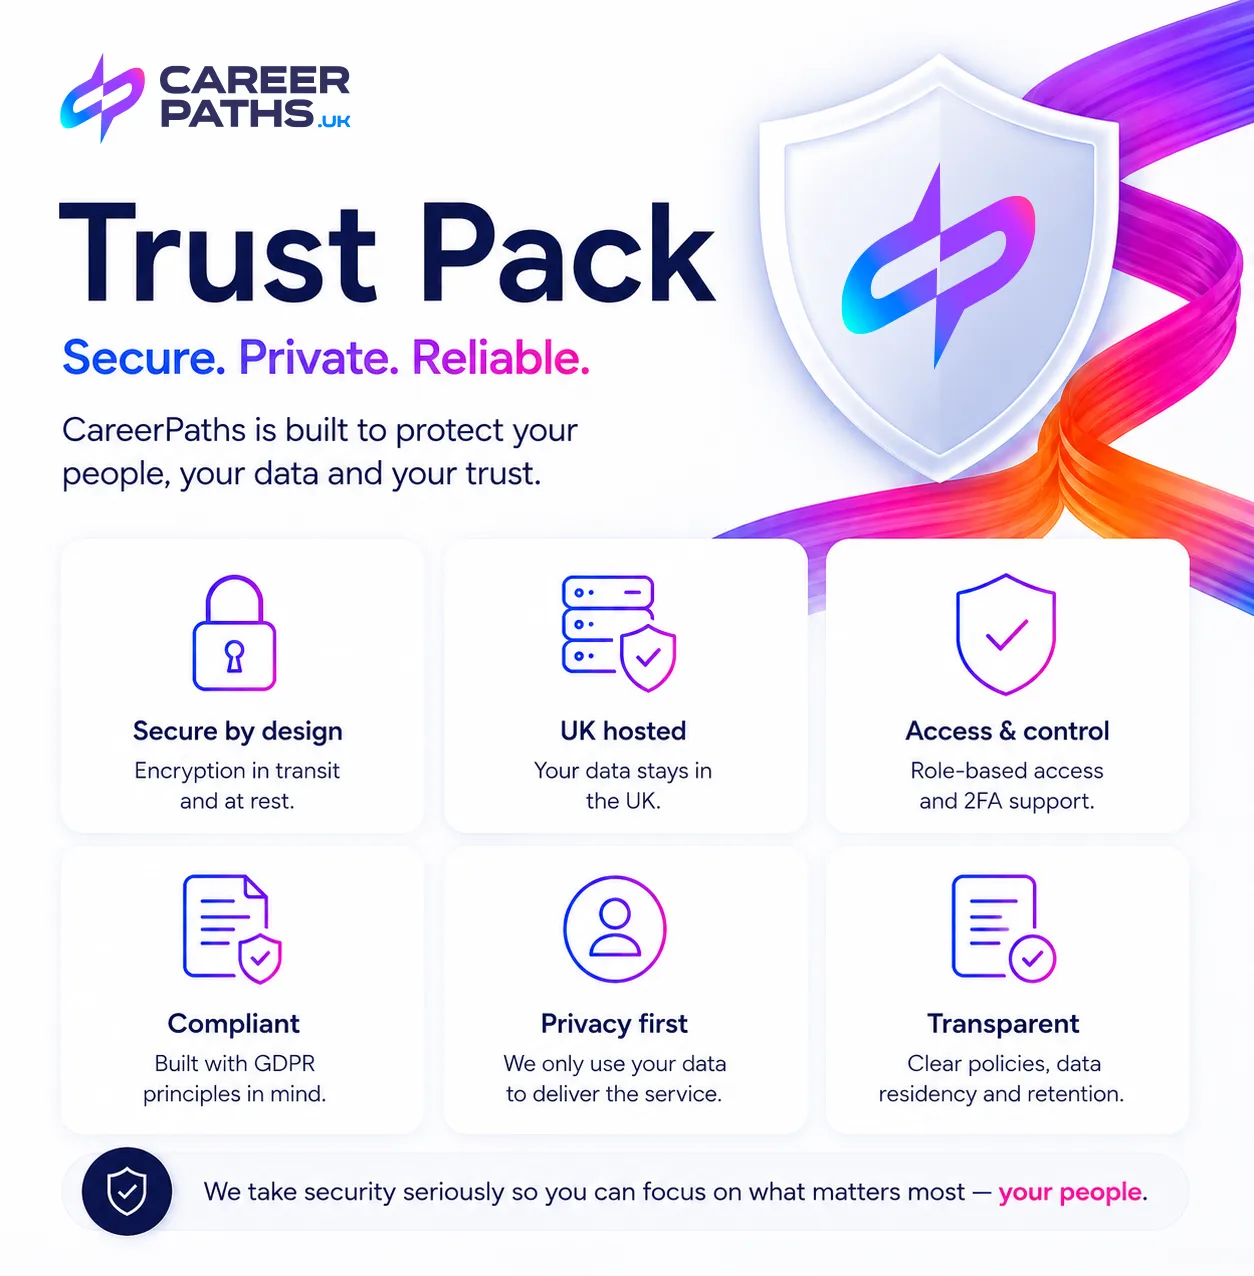
Every organisation runs in its own isolated tenant; data is encrypted in transit and at rest, with field-level encryption on sensitive content, files and private resources; two-factor authentication can be enforced company-wide; and security-sensitive workflows are audit-logged. Full audit-log coverage across every workflow is on our published roadmap.
Also in place.
Role-based access control. Everyone can explore the whole career landscape — that's the point of the platform. What access control governs is administrative permissions: who can edit roles and pathways, who can see reporting, and who can manage other users.
Encryption key management built to support customer-managed keys when we offer them
Private uploaded resources encrypted at rest
Visibility is a design decision, not a settings page
Career conversations are for the people in them
Our commitment is that an administrator can see *whether* career conversations are happening, and never *what was said* — not as a permission we could grant on request, but as how the system is being built.
Cath conversations are confidential.
What someone asks our AI career guide is not surfaced to their manager or to administrators. Organisations receive aggregated, anonymised insight about the kinds of things being asked — never individual conversations.
We don't train on your data
CareerPaths does not use customer data to train its own models.
That is a fixed commitment, not a setting.
Cath is grounded in your own content.
An administrator-managed knowledge base of your roles, pathways and resources. Administrators can additionally enable a general career-guidance fallback for questions your content doesn't cover; it's off unless you turn it on, and clearly distinguished from answers grounded in your material.
Cath is guardrailed to career topics.
She can be switched off entirely.
What we hold, and what we're working towards
We'd rather tell you where we actually are than list standards we're "aligned with". If a certification matters to your procurement process, ask — we'll tell you straight whether we have it, when we expect it, and what we can offer in the meantime.
Cyber Essentials Plus
In progress. Certification against the UK government-backed scheme, independently assessed.
ISO 27001
A larger undertaking, and we're not going to imply it's imminent. We'll do it when customer demand justifies the programme.
What happens meanwhile
The controls in the Trust Pack are evidenced and contractually committed through the DPA.
Documentation
The Paperwork
We maintain the following documents. Tell us what your IT and legal teams need and we'll send it.
Data Processing Agreement
Our UK GDPR Article 28 processor terms, covering processing scope, security measures, sub-processors, international transfers, data subject rights, audit and deletion.
Sub-Processor Register
Every supplier that touches customer data, what they do, what they process and where — including notice periods and the right to object.
Data Residency Statement
Where the application, database, backups and uploaded files are hosted, plus the limited processing that happens elsewhere.
AI and Data Use Statement
How Cath and AI-assisted features work, what leaves your tenant and what doesn’t, and our commitment never to use customer data to train models.
Retention and Off-boarding
What is kept, for how long, what happens at the end of a subscription and how deletion is evidenced.
Employee Transparency Statement
What is kept, for how long, what happens at the end of a subscription and how deletion is evidenced.
DPIA support pack
What is kept, for how long, what happens at the end of a subscription and how deletion is evidenced.
Reporting something
If you believe you've found a security vulnerability, tell us at [email protected]. We'll acknowledge within one business day and keep you updated.
We won't pursue anyone acting in good faith to identify and report a genuine issue.
The questions we get every time.
Useful answers are open on the page. The downloadable documents provide the formal detail behind them.
The platform is hosted in the UK — covering the application, database, uploaded files and backups. Region and configuration are confirmed as part of controlled beta, and evidenced in the Data Residency Statement.
No. CareerPaths does not use customer data to train its own models, and AI features can be disabled entirely. AI requests use the minimum relevant context rather than your database. Our AI and data use statement sets out our provider arrangements in full.
Organisations run in isolated tenants. Data is encrypted in transit and at rest, with field-level encryption on sensitive content, files and private resources. Two-factor authentication can be enforced organisation-wide, and security-sensitive workflows are audit-logged. Full audit-log coverage across every workflow is on our published roadmap.
The participants. Administrators can see whether conversations are happening, for legitimate coverage reporting, but not their content. That's not a permission we could grant on request — it's how the system is being built.
You receive a defined export window for a structured copy of your data. It is then deleted from production and ages out of encrypted backups within the periods stated in the Retention Policy. Written confirmation is available on request.
Yes, on the terms in the DPA: security documentation, penetration-test summaries and certification evidence on request, plus an annual audit right with notice.
We build to a WCAG 2.2 AA target across the platform and the careers websites we deliver. Current supporting evidence can be provided with the Trust Pack.
Questions your security review hasn't covered?
We'd rather answer a hard question now than a complaint later.
Three fields. Then the full pack.
No phone number, no qualification questions and no sales call required. This request is for the reviewer who needs the material, not another marketing sequence.
Request the Trust Pack
Use your work details and we’ll get the documents across to you in 72 hours
"*" indicates required fields
You won’t be sent back to a first-line queue.
Use whichever route makes the review easier for your team.
Available before you buy because we think it should be.
Published pricing, a published roadmap and a published security position are part of the same pattern. If something you need isn’t in the pack, ask. If we don’t do it, we’ll say so.